About me
I am an Identity and Access Management (IAM) Engineer specializing in cloud and hybrid identity security, authentication, and access governance. With a background in security engineering, I design and automate identity controls across Microsoft Entra ID, AWS IAM, Keycloak, and directory systems. My work focuses on building reliable SSO federation, least-privilege authorization, and automated lifecycle workflows that eliminate access drift and improve security posture.
Capabilities & Focus
-
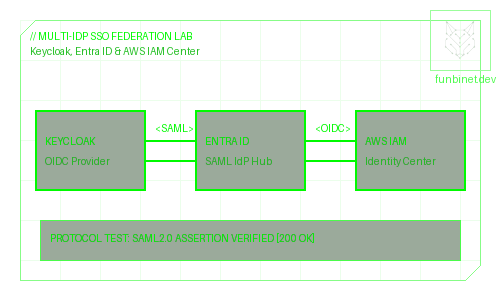
Enterprise SSO & Federation
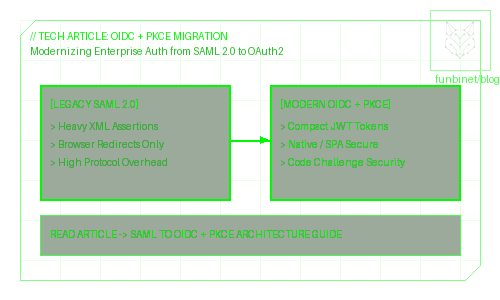
OAuth 2.0, OIDC, SAML 2.0, Keycloak, and Microsoft Entra ID integration with PKCE and token management.
-
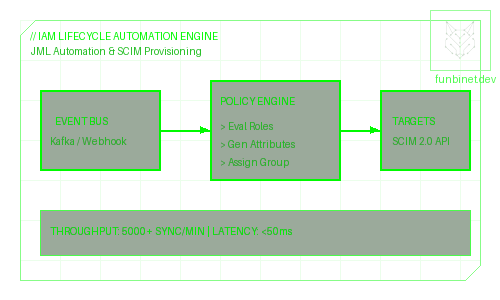
Identity Lifecycle Automation
Joiner-Mover-Leaver workflows, SCIM 2.0 directory sync, and automated access provisioning engines.
-
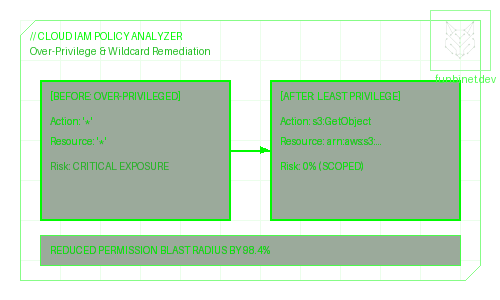
Access Governance & Least Privilege
RBAC/ABAC authorization modeling, access review automation, and entitlement drift detection.
-
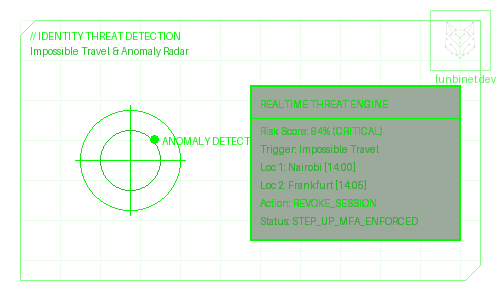
Cloud IAM & Security
AWS IAM policy design, Conditional Access, MFA deployment, and identity threat detection.